
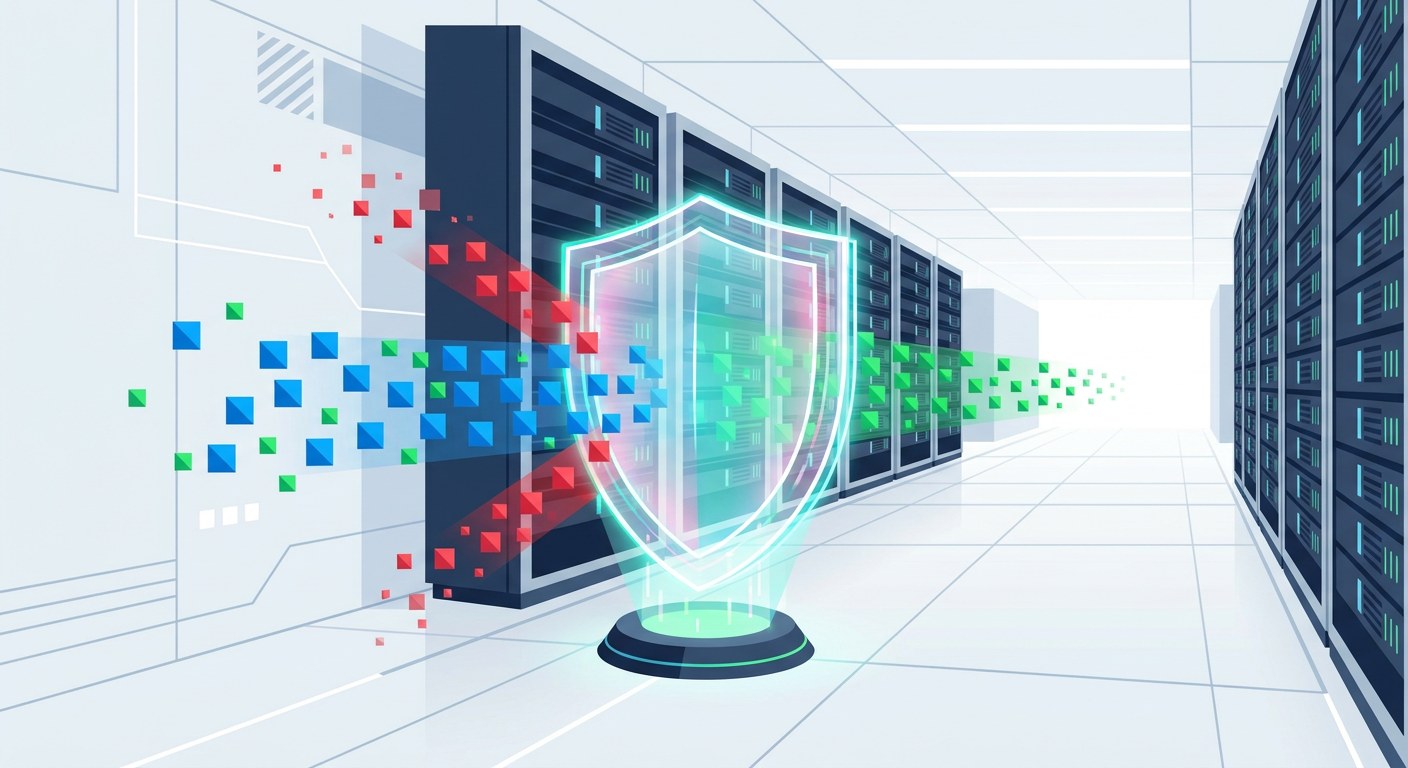
When you type a URL and press Enter, your device does not connect straight to the website: every data packet passes through a filter that decides in fractions of a millisecond whether it should continue, be rewritten, or die in the junk folder. That filter is the firewall, and although its name sounds like a passive barrier, its real job is far more interesting: telling legitimate traffic apart from traffic that tries to sneak in dressed as legitimate.
The underlying problem: all traffic looks alike
On a network, information travels packed in packets (blocks with a header and data). The header says who is sending, who is the destination, through which port and with which protocol. A packet from a normal website and a packet from a vulnerability scanner can have almost identical headers. The challenge for a firewall is not blocking absolute evil, but differentiating behavior from minimal details.
Static filtering: the first generation
The most basic firewall applies packet filtering using static rules: accept or reject based on source IP, destination IP, port and protocol. It is like a doorman who only looks at the ID card: fast, but unable to detect that the document is fake or that the person showing it is an impostor. It also has no sense of context: for it, every packet is an isolated event.
Stateful filtering: memory for connections
The big step forward is the stateful firewall. This one does keep a table of active connections: it records the initial handshake (the famous three-step TCP handshake: SYN, SYN-ACK, ACK), notes which pair of machines is talking and through which ports, and judges each new packet according to that conversation that is already open. So it can let the reply traffic back in for a request that left earlier, without opening the door to connections that were never initiated from inside.
A second layer: inspecting the content
Modern firewalls add a deeper layer. Stateful packet inspection (SPI) checks that every packet fits the expected sequence of its connection, and application firewalls (such as WAFs, Web Application Firewalls) look inside the HTTP data to block attempts at SQL injection or cross-site scripting (XSS), attacks that travel hidden inside legitimate web requests.
Where each type lives
Almost every home router includes a basic firewall with SPI out of the box. In an operating system, the kernel (the core of the system) does the filtering: on Linux it is netfilter/iptables and its successor nftables, and on Windows the Windows Firewall applies rules per program and per port. The cloud and enterprises add WAFs and Next-Generation Firewalls (NGFW), which add intrusion detection and application and user awareness.
The golden rule: order and deny by default
Rules are evaluated in order: the first rule that matches a packet wins, and the rest are ignored. That is why a correct policy design includes a final deny all rule (deny everything not explicitly allowed). The logic is that of an exclusive club: instead of listing what is forbidden, you list the admitted exceptions and everything else stays out. A well-configured firewall does not patch holes: it eliminates them at the root.
Conclusion: the firewall is not a passive wall, but an intelligent filter that reads headers, remembers conversations and, in its most modern versions, inspects the content itself to decide who comes in and who stays at the door.